San Francisco Pillow Test (SFFC 1103.7.6.1) — 75 dBA at every pillow. Deadline passed; fines are being issued.

Get compliant →
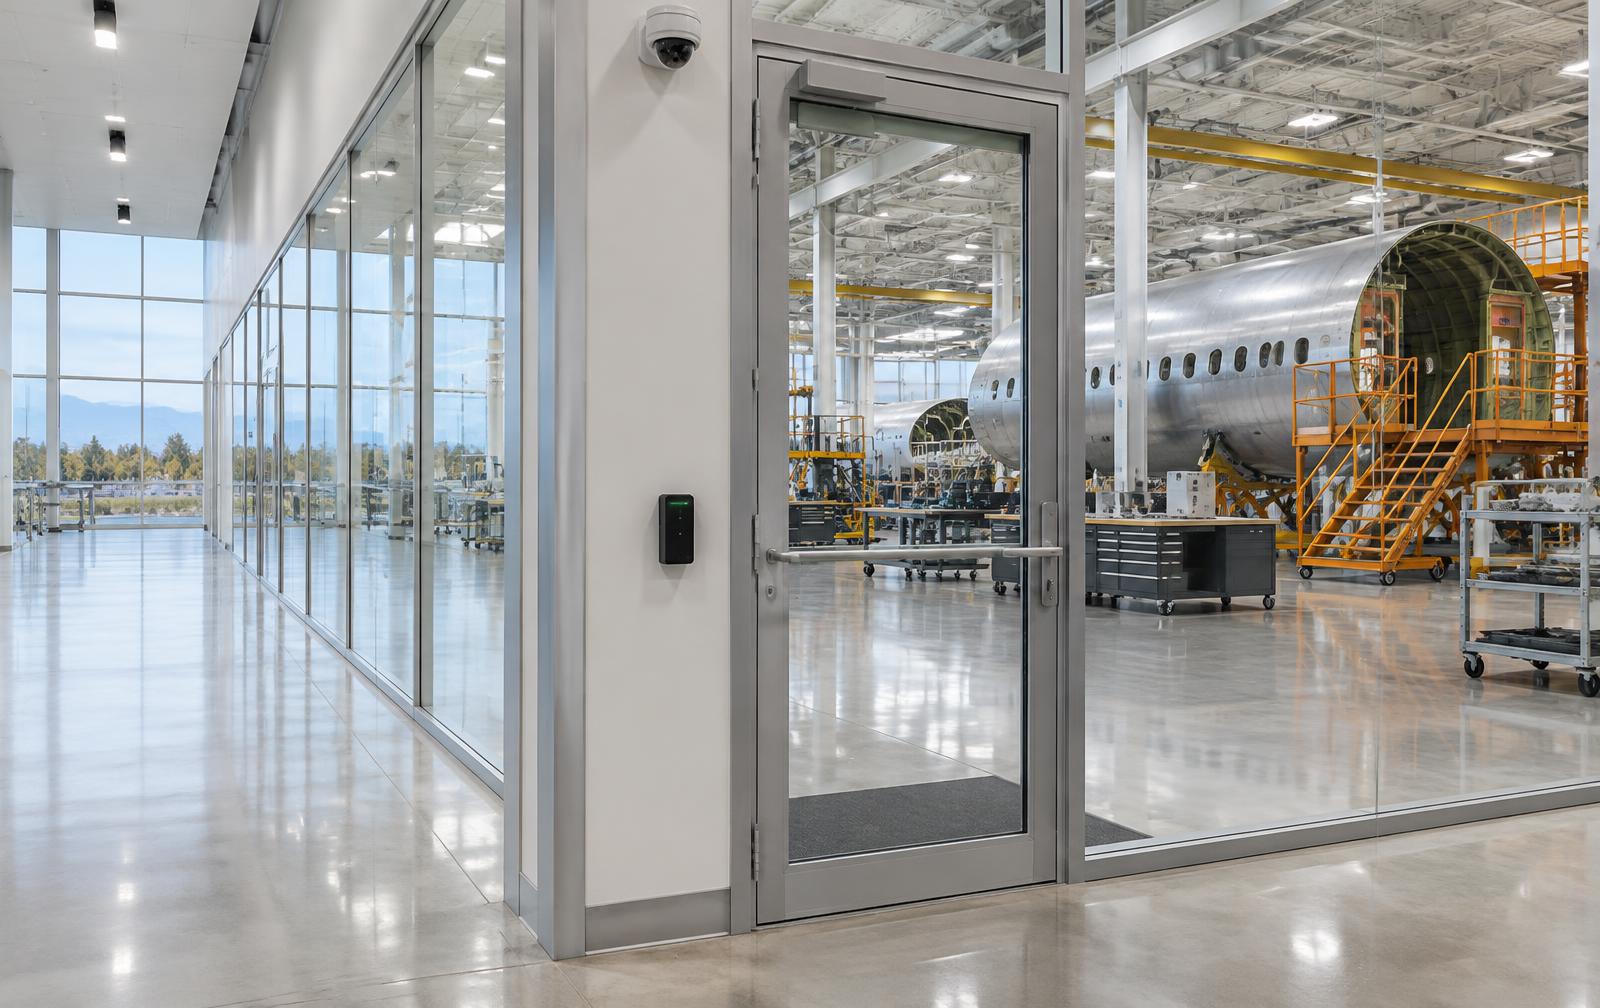
Illustrative aerospace assembly facility with badge-controlled entrance and surveillance camera

Fireside Security · Aerospace & defense facilities

CMMC 2.0 Physical Security
& Compliance Readiness

Physical security installations and complete facility readiness upgrades for California aerospace manufacturers, defense contractors and government subcontractors preparing for CMMC Level 2.

Readiness support—not CMMC certification. Equipment does not guarantee compliance; certification and overall compliance remain your responsibility.

California installation teamsSanta Fe Springs · Hayward · San Mateo · Sacramento

Individual systems or complete scopeInstallation · Integration · Testing · Documentation

Support beyond installationCommercial alarm monitoring · Maintenance · Upgrades

Two ways to work with Fireside

A targeted installation. Or a coordinated facility upgrade.

01

Physical Security Installation

Install or upgrade an individual access control, camera, LPR, intrusion detection or infrastructure system supporting applicable physical security requirements. Start with the highest-priority gap or a defined construction scope.

  • Site review and defined installation scope
  • Equipment configuration and acceptance testing
  • System handover and optional monitoring/maintenance

02

Complete CMMC Physical Security Readiness Package

Coordinate facility assessment, security system design, installation, integration, testing, installation documentation and ongoing maintenance under one agreed physical security scope. Work alongside your IT and compliance teams—not instead of them.

  • Facility assessment and prioritized physical security gaps
  • Integrated door, camera, perimeter and infrastructure plan
  • Test results, system records and maintenance planning

The complete package covers physical security readiness only. It does not include CMMC certification, a C3PAO assessment, or the customer's complete cybersecurity compliance program.

Aerospace security systems

Protect people, restricted areas & infrastructure

Access control

DMP · Brivo · PDK · UniFi Access

Electronic credentials, restricted-area permissions, door monitoring and physical access logs. Plan authorized users, visitor access and credential revocation with your security team.

Explore access control

Video surveillance

Turing AI · UniFi Protect

Camera coverage for entrances, production areas and facility monitoring. Plan secure recording, retention, retrieval permissions and remote access against your approved architecture.

Explore video surveillance

License plate recognition

Vehicle entrances & perimeter

LPR cameras support vehicle event records, entrance monitoring and perimeter investigations. Plate recognition supplements—not replaces—personnel authorization and visitor controls.

Explore license plate recognition

Intrusion detection

DMP commercial alarm systems

Door contacts, motion detection and intrusion monitoring for restricted rooms, loading docks and after-hours activity. Coordinate alarm response and dispatch instructions with the facility.

Explore intrusion detection

Secure infrastructure

Structured cabling · Fiber · Locked racks

Protected cable pathways, fiber connectivity, locked network racks and security network infrastructure. Coordinate segmentation, administrative access and network hardening with customer IT.

Explore secure infrastructure

Maintenance & monitoring

Ongoing support & system upgrades

Commercial alarm monitoring, periodic inspections, maintenance, repairs and upgrades. Keep devices, access permissions and test records aligned with your changing facility and service agreement.

Explore maintenance & monitoring

CMMC Level 2 · NIST SP 800-171

How physical systems support the protection requirements

CMMC Level 2 uses the 110 requirements in NIST SP 800-171 Revision 2. The six physical protection requirements below are one part of that broader program. Confirm the current contract, CUI boundary and assessment requirements with your compliance lead; NIST's newer Revision 3 publication is not interchangeable with this CMMC baseline.

PE · 3.10.1

Restrict physical access

Limit access to organizational systems, equipment and operating environments to authorized individuals. Door readers, restricted-area permissions and locked network racks support your documented authorization process.

PE · 3.10.2

Protect & monitor the facility

Protect and monitor the physical facility and supporting infrastructure. Cameras, door monitoring, intrusion detection and protected cabling can support this outcome; no particular camera, alarm or LPR brand is mandated by this requirement.

PE · 3.10.3

Escort & monitor visitors

Escort visitors and monitor their activity. Temporary credentials and video coverage can support oversight, but they do not replace your visitor authorization, escort procedures and staff responsibilities.

PE · 3.10.4

Maintain physical access logs

Maintain audit logs of physical access. Electronic access events can support these records when the system is properly configured and your team manages log review, retention, time settings and access to records.

PE · 3.10.5

Manage physical access devices

Control and manage physical access devices, including keys, badges and credentials. Issuance, approved permissions, lost-badge response and prompt revocation remain part of the customer's operating procedures.

PE · 3.10.6

Safeguard alternate work sites

Enforce safeguarding measures for controlled unclassified information (CUI) at alternate work sites. A main-facility installation does not resolve remote-work protections; your team must define and implement those measures separately.

Your organization defines authorized personnel, maintains visitor procedures, manages credentials and reviews evidence. Fireside supplies the contracted physical systems and installation records; your assessor evaluates the implementation and overall compliance.

Official references: DoD CMMC documentation and Level 2 assessment guide · NIST SP 800-171 Revision 2
From assessment to ongoing operations

An evidence-ready installation starts with a defined scope

Review facility access points, production areas, shipping entrances, server rooms and security equipment with your facility, IT and compliance leads. Define the controlled areas and approved architecture before selecting equipment.

Cloud services, AI features, remote access and recordings need customer review for data handling, contract restrictions and the assessment boundary. Brand selection alone does not establish that a deployment is suitable for CUI.

  1. 01

    Assess — walk the facility and prioritize physical security gaps.

  2. 02

    Design — define coverage, door schedules and approved integrations.

  3. 03

    Install & test — configure equipment and verify agreed system operation.

  4. 04

    Document & maintain — hand over system records and plan ongoing support.

Installation quote or facility assessment

Plan your CMMC physical security readiness project

Tell us about your facility, existing systems and physical security priorities. We help aerospace manufacturers, defense contractors and government subcontractors scope installations, coordinated upgrades and recurring maintenance or monitoring.

Requesting an installation quote

Do not include CUI, passwords, sensitive facility drawings, access codes or detailed vulnerabilities in this public form. We can coordinate an appropriate information-sharing process after initial contact.

Prefer to talk? (888) 810-2336

Illustrative aerospace manufacturing entrance with badge reader, camera and aircraft assembly floor
Illustrative aerospace facility—not a Fireside customer location.

Contact a security specialist

CMMC physical security project

Or call (888) 810-2336 for immediate service.

CMMC physical security: frequently asked questions

Is Fireside Security CMMC certified?

This service is physical security installation and readiness support, not a claim that Fireside Security is CMMC certified. Fireside does not issue CMMC certifications. Certification and overall compliance remain the customer's responsibility through the applicable assessment process.

Does access control or a camera system guarantee CMMC Level 2 compliance?

No. Equipment supports selected physical protection requirements only when configured, operated and documented appropriately. CMMC Level 2 also covers many cybersecurity and organizational requirements outside this installation scope. No equipment brand automatically guarantees compliance.

Which NIST SP 800-171 requirements does this service support?

The physical protection family in NIST SP 800-171 Revision 2 covers restricted access (3.10.1), facility protection and monitoring (3.10.2), escorted and monitored visitors (3.10.3), physical access logs (3.10.4), access device management (3.10.5), and alternate work-site safeguards (3.10.6). CMMC Level 2 uses the Revision 2 baseline; confirm current contract and assessment requirements with your compliance lead. Main-facility systems do not by themselves address alternate work sites.

Can we request an individual installation rather than a complete package?

Yes. Request a standalone access control, surveillance, LPR, intrusion detection or security infrastructure installation. Alternatively, the Complete CMMC Physical Security Readiness Package coordinates a facility assessment, design, installation, integration, testing, installation documentation and ongoing maintenance within the agreed physical security scope.

Which access control, surveillance and alarm platforms do you install?

Fireside offers DMP, Brivo, PDK and UniFi Access for access control; Turing AI and UniFi Protect for surveillance; and DMP commercial intrusion detection systems. Platform selection, integrations, recording architecture and credential workflows are evaluated against the facility and customer's security requirements, not a blanket compliance claim.

Are license plate recognition cameras required by CMMC?

LPR is not a universal CMMC Level 2 requirement. It can support vehicle entrance monitoring and perimeter investigations where appropriate. A plate event is not proof of an individual's authorization and does not replace personnel access control, visitor procedures or facility access logs.

What documentation can Fireside provide for readiness?

Depending on the proposal, deliverables can include a device inventory, coverage and door schedules, configuration records, agreed access permissions, system test results, maintenance records and instructions for retrieving supported access events. Your compliance team owns policies, the system security plan, evidence review and assessment submissions. Do not send CUI, passwords or sensitive facility drawings through this public form.

Do you provide ongoing alarm monitoring and maintenance?

Yes. Contracted services can include commercial alarm monitoring, periodic system inspections, maintenance, repairs and upgrades. Monitoring coverage, dispatch instructions, system compatibility and maintenance scope are confirmed in the service agreement. Alarm response follows that agreement and does not guarantee law-enforcement response.